Honeypot
A fake target set up on purpose to attract attackers, so you can spot them and watch them.
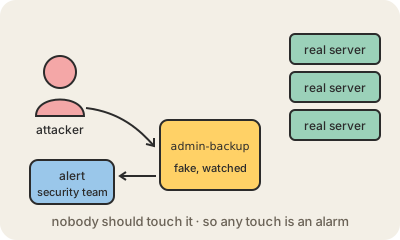
A honeypot is a computer, service or file that looks real and valuable but exists only to be attacked. No legitimate user has any reason to touch it, so any connection to it is suspicious by definition. That makes it a very quiet, very reliable alarm: instead of sifting through millions of normal events looking for an intruder, you wait for someone to bite.
Some honeypots are research tools. A security team leaves a deliberately weak server open on the internet and records everything that happens: which passwords bots try, what malware they drop, which commands a human attacker types. Many of the reports you read about new botnets come from this kind of trap. A network of them is called a honeynet.
Inside companies the goal is early warning. A fake server named something like payroll-db or admin-backup, a fake admin account, or a honeytoken (also called a canary token): a fake password, API key or document planted where only an intruder would look. If it is ever used or opened, an alert goes straight to the security team. Honeypots must be isolated so an attacker cannot use them as a stepping stone, and they only catch attackers who come looking, so they complement normal defenses rather than replace them.
Keep in mind
- A decoy with no legitimate use: anyone who touches it is a suspect.
- Research honeypots study attackers; company honeypots raise early alarms.
- Honeytokens are fake credentials or files that alert when used or opened.
- Must be isolated, and only catch attackers who go looking.