Amazon Inspector
An AWS service that keeps scanning your servers and code for known vulnerabilities.
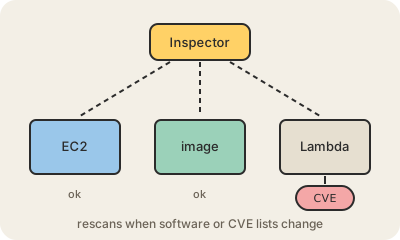
Amazon Inspector is AWS's vulnerability management service. It looks at the software running in your account and checks it against databases of known security holes, the CVEs. If a server has an old version of a library with a published flaw, Inspector tells you.
It discovers what to scan on its own: EC2 instances, container images stored in Amazon ECR, and Lambda functions. You do not schedule scans. It rescans when something changes, such as a new package being installed, or when a new CVE is published that affects software you already run. For EC2 it also checks network reachability, flagging, for example, a port that is open to the internet when it probably should not be.
Each issue becomes a finding with the affected resource, a severity score and how to fix it, usually which version to upgrade to. When you patch, Inspector notices and closes the finding. Its results also flow into AWS Security Hub, where they are combined with other signals.
Keep in mind
- Scans EC2 instances, ECR container images and Lambda functions.
- Rescans automatically when software changes or a new CVE appears.
- Each finding includes severity and a suggested fix.
- Closes findings by itself once the vulnerability is patched.