Amazon ECR
A private warehouse on AWS for your container images, ready to be deployed.
ECR (Elastic Container Registry) is where you store container images on AWS. An image is the packaged version of an app: the code, the libraries and the settings it needs, frozen in one file that any machine can run. Before you can run it on AWS, the image has to live somewhere AWS can fetch it from, and that place is a container registry.
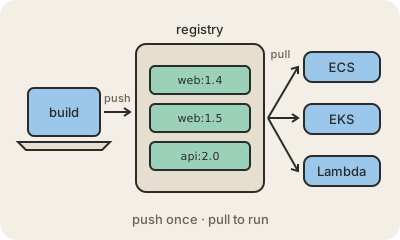
The flow is short. A developer or a build pipeline creates the image with Docker, tags it with a version like web:1.4.2, and pushes it to an ECR repository. Then Amazon ECS, Amazon EKS or AWS Lambda pulls that exact version and starts it. Access is controlled with IAM, so only the people and services you allow can push or pull.
ECR also does some housekeeping: it can scan images for known vulnerabilities in the software they contain, and lifecycle rules can delete old versions automatically so the repository does not grow forever. There is a public side too, for sharing images with anyone, but most teams use ECR as the private, nearby copy of what they deploy.
Keep in mind
- Stores and versions container images inside your AWS account.
- You push images to it; ECS, EKS and Lambda pull them to run.
- Access goes through IAM; images are private by default.
- Can scan images for known vulnerabilities and expire old versions.