AWS Config
An AWS service that records how your resources are set up and checks them against rules.
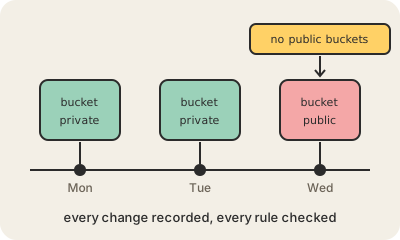
AWS Config keeps an inventory of the resources in your AWS account, such as EC2 instances, S3 buckets, security groups or VPCs, and records every change to their settings over time. You can look at any resource and see what it looked like last Tuesday, who changed it (by linking to CloudTrail), and which other resources it is connected to.
On top of that history you add rules. A rule describes how something should be configured: "S3 buckets must not be public", "EBS volumes must be encrypted", "only approved instance types". Config evaluates your resources against the rules whenever they change and marks each one compliant or noncompliant. AWS provides many ready-made managed rules, and you can write your own. Groups of rules for a standard can be deployed together as a conformance pack.
It matters because cloud resources change constantly and many people can change them. Auditors ask "prove this was encrypted all year", and security teams want to know the minute someone opens a database to the internet. Config answers both. It can also trigger automatic fixes, but its main job is to record and evaluate.
Keep in mind
- Inventory plus change history of the settings of your AWS resources.
- Rules mark each resource as compliant or noncompliant.
- Conformance packs bundle rules for a standard or policy.
- Used for audits, security checks and catching risky changes fast.