AWS IAM Identity Center
One sign-in for a company's people to reach all its AWS accounts and apps.
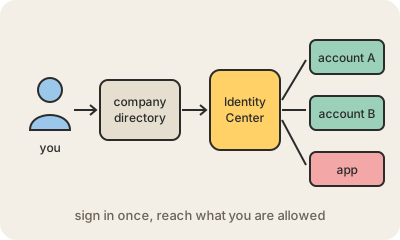
AWS IAM Identity Center is where a company manages how its own staff get into AWS. Instead of creating a separate IAM user with a password in every AWS account, you connect the directory you already use (Microsoft Entra ID, Okta, Google Workspace and others) or create users right in Identity Center. People then sign in once and see a portal with the accounts and applications they are allowed to use.
Access is described with permission sets: a named bundle of permissions such as "read-only" or "database admin". You assign a group, say "data team", a permission set in specific accounts, and Identity Center creates the matching IAM roles behind the scenes. When someone leaves the company and is disabled in the directory, their AWS access goes with it. Command-line tools get short-lived credentials too, so nobody needs long-term access keys on their laptop.
It used to be called AWS Single Sign-On (AWS SSO) and was renamed in 2022. It works hand in hand with AWS Organizations, which groups the accounts it gives access to. IAM is still the engine that decides what each role can do; Identity Center is the front door for people.
Keep in mind
- Single sign-on for a workforce across many AWS accounts and apps.
- Connects to an existing directory or keeps its own users.
- Permission sets define what a group can do in each account.
- Formerly AWS Single Sign-On; renamed in 2022.