Amazon Macie
An AWS service that finds sensitive data in your S3 buckets and flags risky buckets.
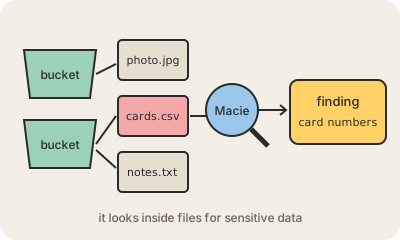
Amazon Macie is a data security service focused on Amazon S3. Companies pile up years of files in buckets: exports, logs, backups, spreadsheets someone uploaded once. Nobody remembers which of them contain customer names, ID numbers, credit card numbers or passwords. Macie goes looking for that.
It does two jobs. First, it keeps an inventory of your buckets and watches how they are configured, for example whether one becomes publicly accessible or is not encrypted. Second, it opens objects and inspects their contents, using pattern matching and machine learning to recognize sensitive data. You can let it sample buckets automatically and continuously, or run a discovery job over specific buckets. You can also add your own patterns, like the format of your internal customer IDs.
Each problem it finds becomes a finding that you review in the console or send elsewhere, such as Amazon EventBridge for automation or AWS Security Hub for a combined view. Macie is especially useful for privacy rules like GDPR: you cannot protect personal data if you do not know where it is.
Keep in mind
- Works on data stored in Amazon S3.
- Detects sensitive data with built-in patterns, machine learning and your own custom rules.
- Also flags bucket risks, like public access or missing encryption.
- It reports findings; fixing the problem is up to you or your automation.